Security and Behavioral AI Projects
Our security-focused research explores behavioral biometrics, continuous authentication, and adversarial robustness to strengthen user privacy and trust in modern computing systems. By harnessing motion sensors, touch data, and deep learning, we create lightweight, real-time authentication frameworks that safeguard smartphones even under adversarial conditions. These efforts extend to dynamic ensemble learning and decision-level fusion, enabling adaptive and explainable AI models across high-risk domains like cybersecurity, finance, and mobile platforms.
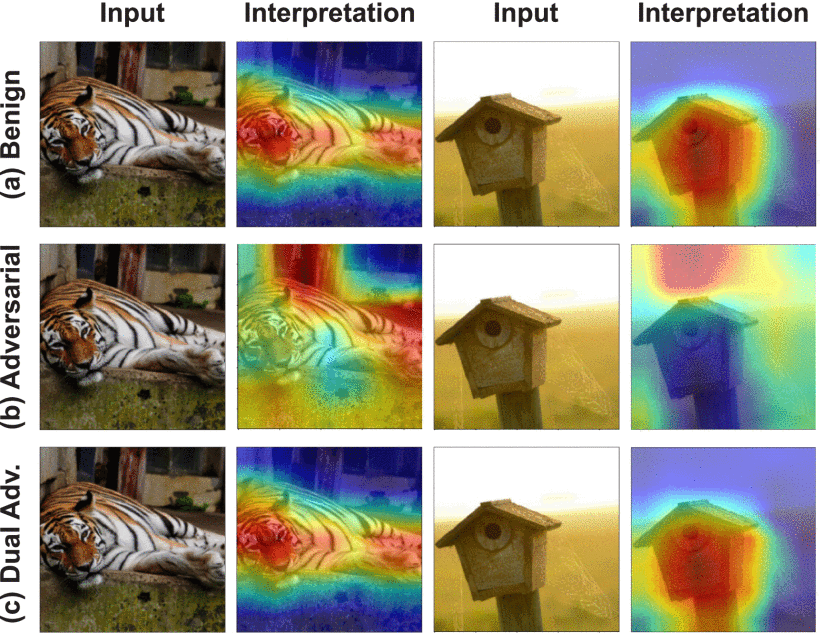
The growing integration of deep learning (DL) models into high-stakes domains, such as healthcare, finance, and autonomous systems, has made interpretability a cornerstone of trustworthy AI. Interpretable Deep Learning Systems (IDLSes), which combine powerful neural networks with interpretation models, aim to provide transparency into the decision-making process. However, the assumption that interpretation inherently adds security has recently been challenged.
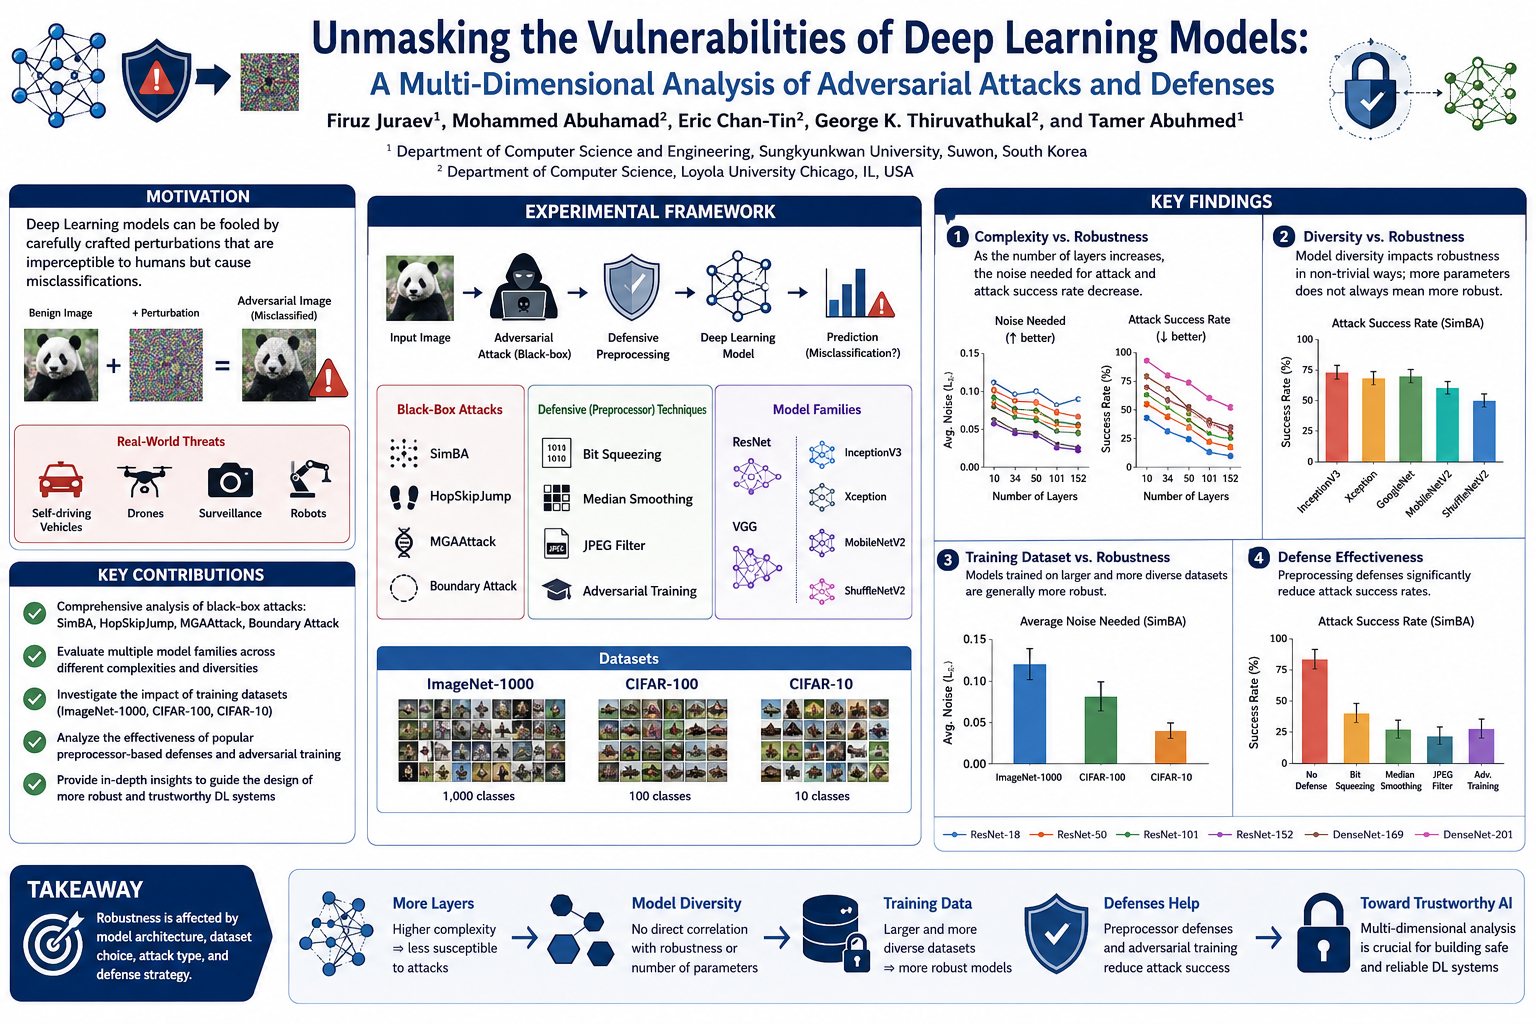
Adversarial attacks pose a serious challenge to the reliability and security of deep learning (DL) models. These attacks, often crafted by introducing imperceptible perturbations to input data, can cause models to make incorrect predictions with high confidence. As a result, understanding and mitigating such threats has become a critical area of research in the field of trustworthy AI. Defenses against adversarial attacks range from input preprocessing and adversarial training to robust model design, yet no single approach has proven universally effective.
The dynamic evolution of malware, combined with increasingly sophisticated evasion techniques such as packing, obfuscation, and polymorphism, presents a significant challenge to conventional security mechanisms. Machine learning (ML)-based malware detection systems are widely adopted for their ability to generalize and automate malware identification, yet they remain susceptible to adversarial threats. InfoLab at SKKU investigates robust, interpretable detection pipelines—spanning spectral control-flow-graph analysis, the effects of packing on ML detectors, and visualization-based feature fusion—to identify evasive and morphed malware across desktop and mobile platforms.
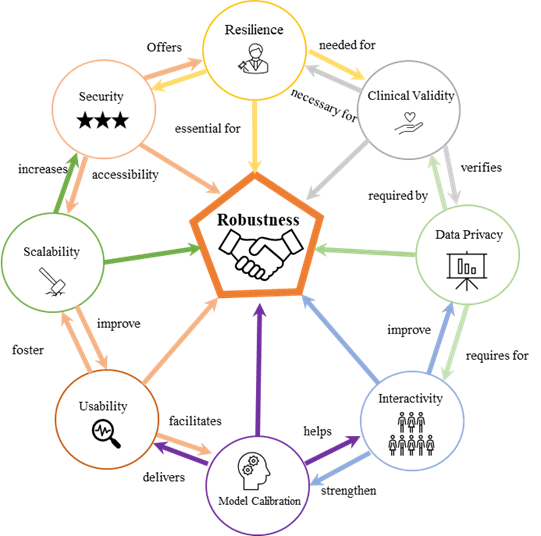
The project seeks to address the growing need for transparency, accountability, and interpretability in artificial intelligence (AI) systems used in healthcare. As deep learning and other machine learning techniques become integral to medical diagnostics, prognosis, and treatment planning, the “black-box” nature of many AI models poses significant challenges for clinical adoption, regulatory approval, and patient trust.
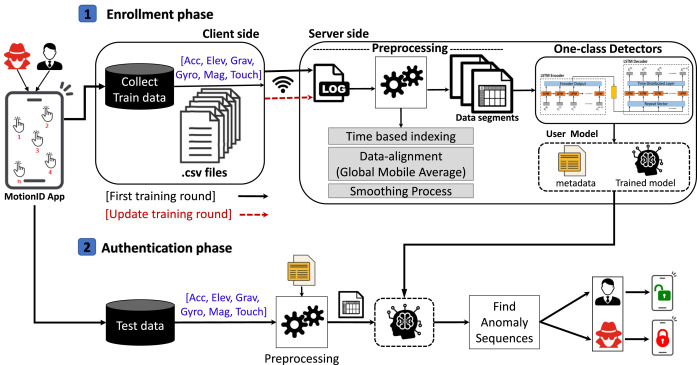
Traditional authentication methods—such as passwords, PINs, and even biometric systems (fingerprint, facial recognition)—typically secure mobile devices only at the point of entry. However, they fail to offer protection throughout a session, leaving devices vulnerable to unauthorized access when unattended. To bridge this security gap, the research group InfoLab at Sungkyunkwan University (SKKU) has led a series of studies on continuous, sensor-based, and adversarially-aware user authentication mechanisms.
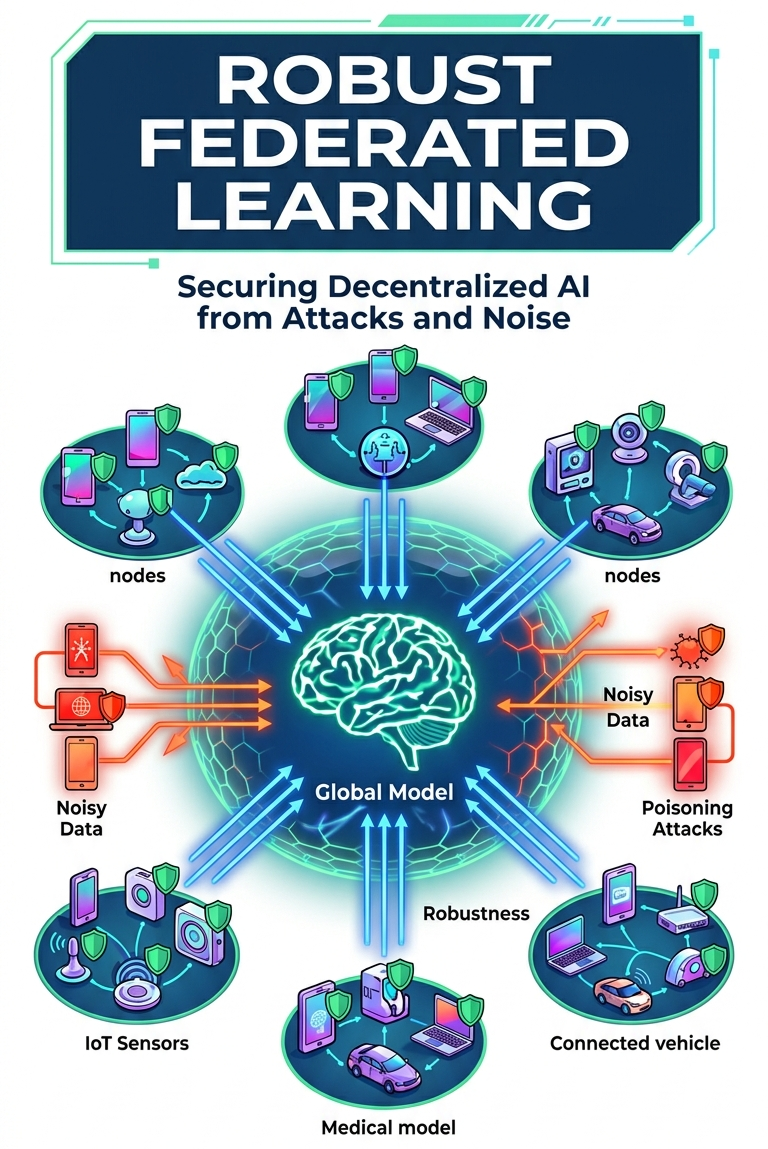
Federated learning lets many clients collaboratively train a shared model without exchanging raw data, making it ideal for privacy-sensitive domains like healthcare and finance. But because the server never sees client data, malicious participants can quietly corrupt the global model through data- and model-poisoning attacks. InfoLab at SKKU investigates how robust federated learning really is once clean, identically distributed data is no longer assumed—studying how poisoning attacks behave under realistic client data heterogeneity (non-IID settings) and how robust-aggregation defenses must adapt when honest clients already look very different from one another.
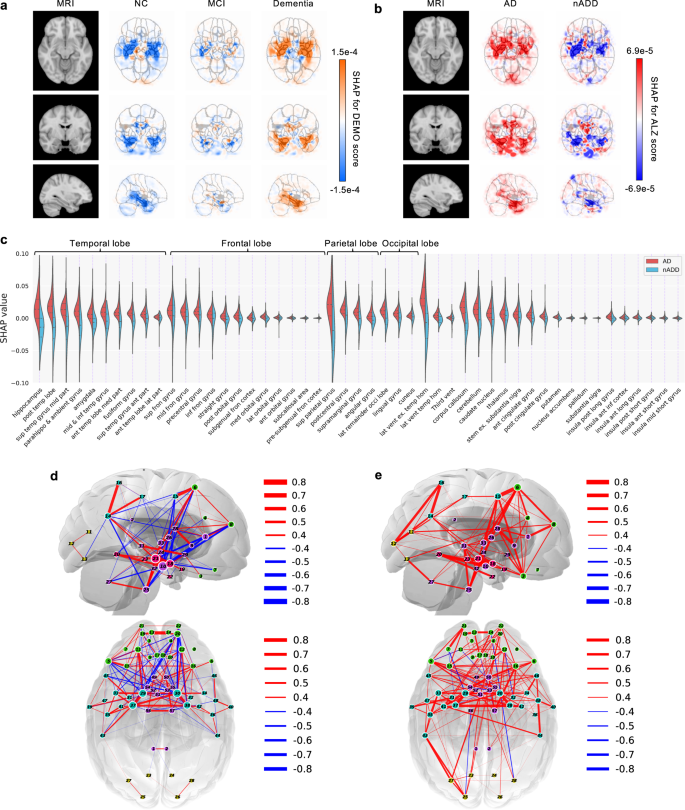
Alzheimer’s disease (AD) is the most common form of dementia, affecting millions globally, yet early and accurate detection remains a critical challenge. InfoLab leads a research program combining multimodal neuroimaging data (MRI, PET), clinical assessments, and genetic biomarkers with state-of-the-art deep learning to detect and track AD progression. Our models incorporate explainable AI techniques that highlight which brain regions and biomarkers drive predictions, enabling clinicians to interpret and trust model outputs. We further harden these systems against adversarial perturbations to ensure diagnostic robustness in real-world clinical settings.
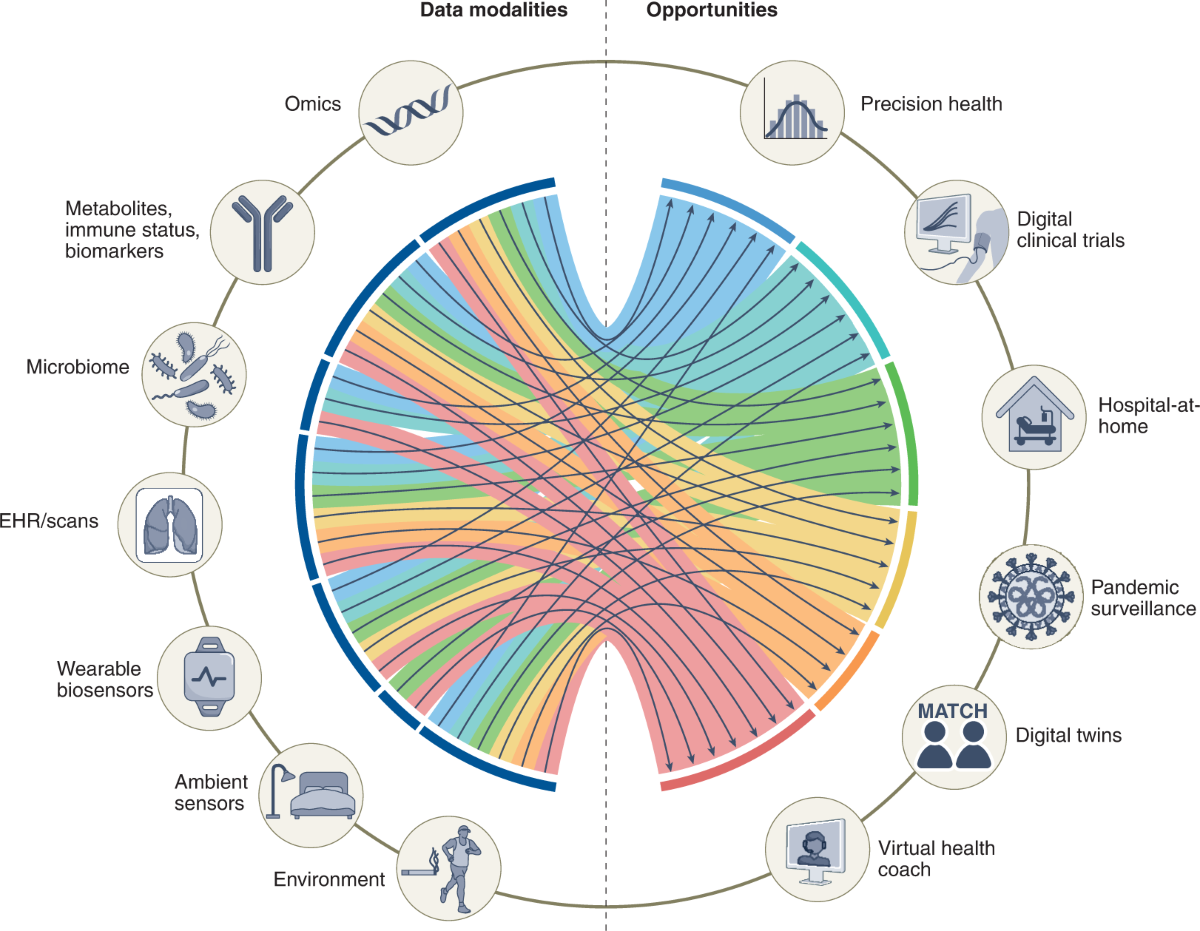
Clinical decision-making demands the integration of heterogeneous data sources—lab results, imaging, clinical notes, vital signs, and genomic data—that no single model handles optimally. InfoLab develops dynamic ensemble frameworks that adaptively combine specialized sub-models at late fusion stages, weighting their contributions based on data availability and uncertainty. Each ensemble decision is paired with an explainability layer that surfaces the evidence supporting the recommendation, enabling clinicians to validate, override, or defer to the system with confidence. Applications span depression severity assessment, sepsis risk stratification, and post-surgical outcome prediction.
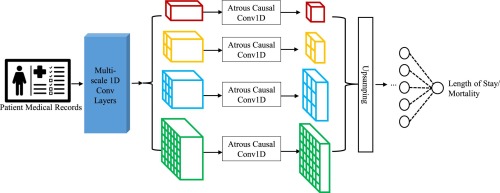
Predicting patient outcomes in the Intensive Care Unit (ICU)—mortality risk, length of stay, and deterioration events—can save lives and optimize resource allocation, yet the complexity of clinical time-series data makes this a formidable modeling challenge. InfoLab applies dynamic ensemble methods that fuse longitudinal vital signs, lab measurements, medication histories, and diagnostic codes from large-scale ICU databases such as MIMIC and eICU. Our explainable models generate patient-level risk scores alongside interpretable feature attributions, giving intensivists actionable insight into which clinical indicators are driving the prediction at each point in time.
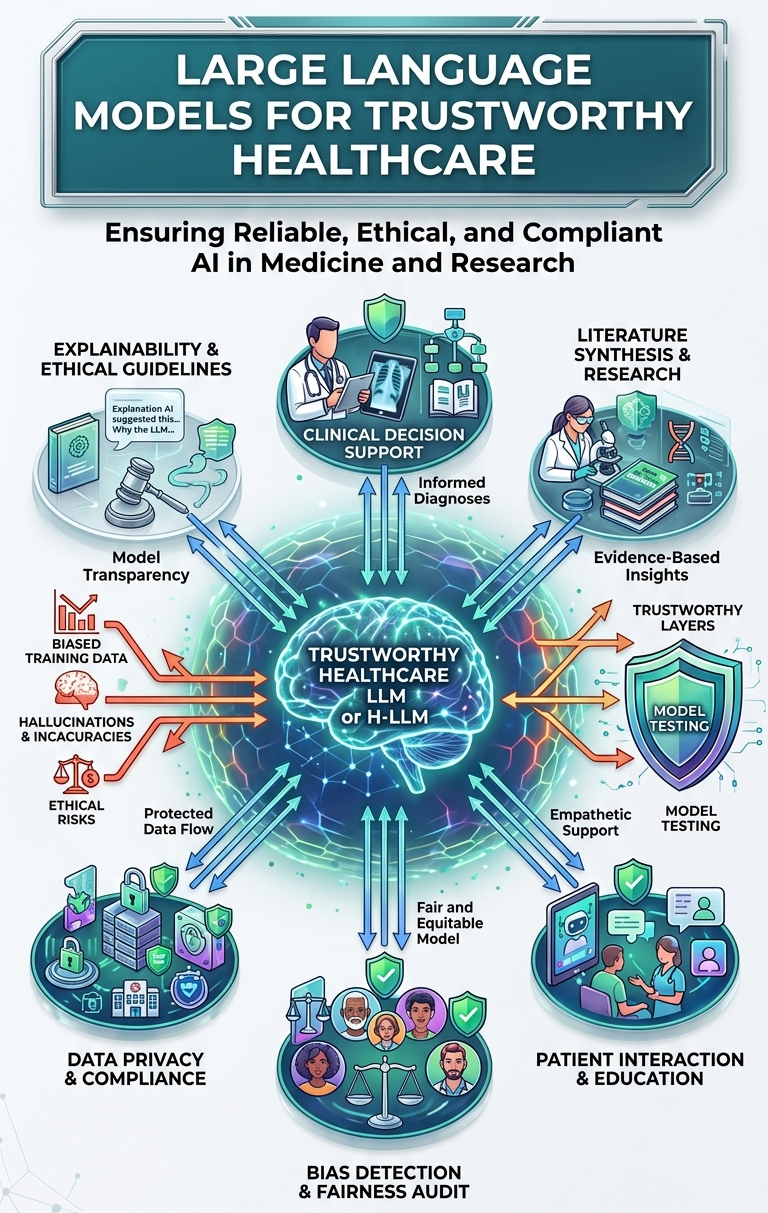
Large language models are reshaping how clinical knowledge is accessed, explained, and acted upon—but healthcare is precisely where hallucination, opacity, and unsafe recommendations are least acceptable. InfoLab at SKKU develops and evaluates LLM-powered systems that pair the fluency of modern language models with knowledge grounding, explainability, and responsible-AI safeguards. Our work spans smart pharmacy systems for drug safety, knowledge-augmented explainable chatbots that curb hallucination, and LLM-based clinical outcome prediction, all designed to be accurate, transparent, and safe enough for real clinical and pharmacy workflows.
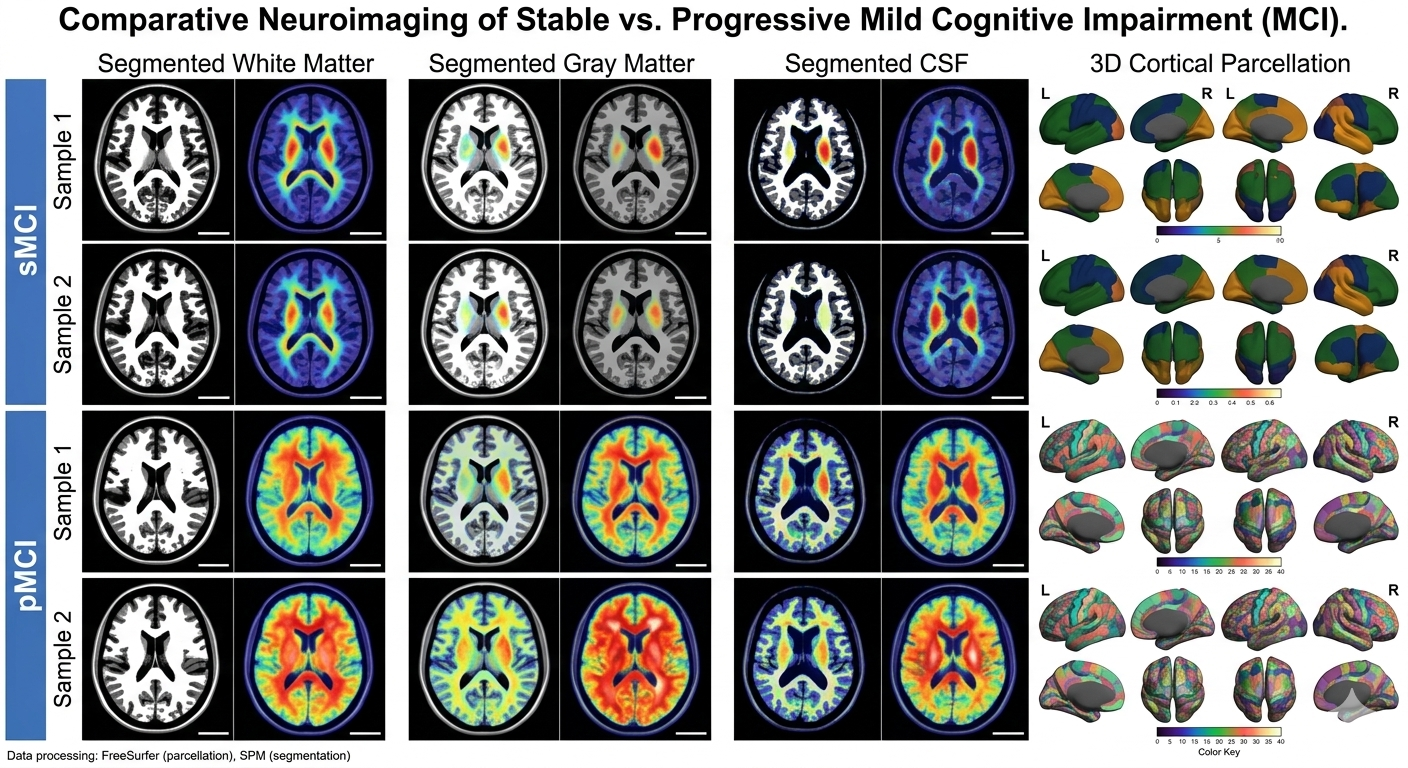
Deep learning now matches clinicians on many diagnostic and screening tasks, yet adoption stalls when models cannot explain their decisions or generalize beyond curated benchmarks. Across conditions—from sight-threatening eye disease to chronic kidney and bone disorders—InfoLab at SKKU builds diagnostic systems that are accurate, robust, and interpretable. This work unifies explainable AI for disease diagnosis and medical imaging beyond neurodegenerative disease, combining transfer learning, hybrid CNN–Transformer architectures, and ensembles with clinician-inspectable explanations across diabetic retinopathy grading, chronic kidney disease detection, osteoporosis screening, and skin-cancer staging.